Endpoint security problems rarely come from one weakness alone. An employee laptop may be fully patched but still run unauthorised software. Another device may have strong malware protection but allow uncontrolled USB transfers. A remote endpoint may contain sensitive files while operating outside the corporate network for long periods.
This is why endpoint security should be designed as a set of coordinated controls rather than a single product decision. Organisations need to understand which endpoint risks they are trying to reduce, which controls address those risks, and where different policies are required for users, departments, servers and remote devices.
What is layered endpoint security?
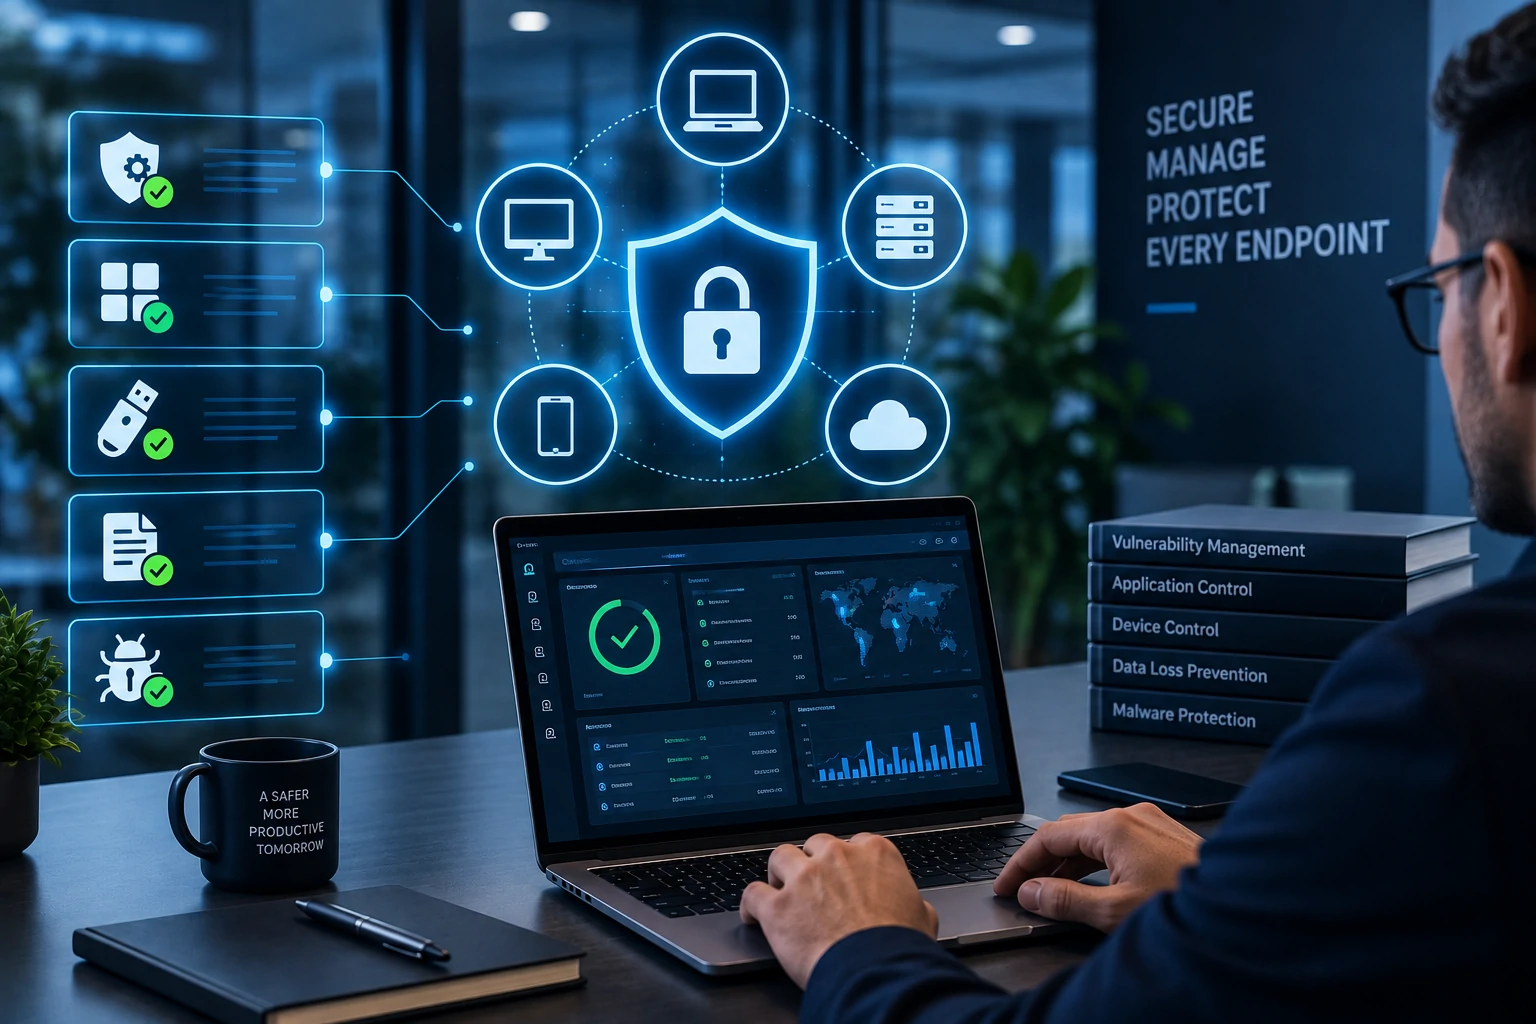
Layered endpoint security combines several complementary controls to reduce different types of endpoint risk. These controls may include vulnerability management, patching, application control, peripheral device restrictions, data loss prevention, malware protection and endpoint configuration management.
The purpose is not to deploy as many tools as possible. Each control should address a defined security problem.
For example, ManageEngine Vulnerability Manager Plus focuses on identifying, assessing, prioritising and remediating vulnerabilities across supported endpoints and systems. Its capabilities include vulnerability assessment, risk prioritisation, patch management, security configuration management, high risk software auditing and additional remediation controls.
Where the organisation needs protection beyond vulnerability remediation, other ManageEngine endpoint security products address different parts of the attack surface.
Why is patching alone not enough for endpoint security?
Patch management is essential, but an endpoint can be fully updated and still present security exposure.
An employee might install an unauthorised remote access application. A user could copy confidential information to removable media. A malicious process might execute through an approved operating system component. Sensitive files could be uploaded to an unauthorised web service. None of these scenarios is solved simply by installing operating system updates.
This does not reduce the importance of patching. It shows why patching should operate alongside controls that address software execution, peripherals, sensitive data and malicious behaviour.
A practical endpoint security scenario
Consider a company managing 500 endpoints across a head office, branch locations and remote employees.
One finance laptop contains an outdated browser extension and several missing third party application updates. Another device has an unsupported remote access tool installed. A user in operations occasionally transfers files to USB drives for field work. The finance team handles sensitive spreadsheets, while remote staff routinely connect from networks outside the office.
A single security control cannot address all of these conditions effectively.
- Vulnerability assessment is required to identify missing updates and insecure configurations.
- Application control may be required to prevent unapproved software from executing.
- Peripheral controls may be needed to manage removable devices and file transfers.
- Data loss prevention may be required where sensitive information moves through USB, email, browsers or other channels.
- Malware protection is needed to detect and respond to malicious behaviour on endpoints.
The correct endpoint security architecture therefore begins with risk mapping rather than product selection.
Tech Wave implementation recommendation: classify endpoints into groups before applying security policies. Employee laptops, developer workstations, point of service devices and production servers may have very different software requirements and change sensitivity. One strict policy applied everywhere can interrupt legitimate work, while one permissive policy applied everywhere may leave avoidable exposure.
A practical workflow for strengthening endpoint security
A structured endpoint security programme can follow these stages:
- Inventory: Identify managed endpoints, operating systems, applications, users and business roles.
- Assess: Scan for vulnerabilities, missing patches, insecure configurations and high risk software.
- Prioritise: Rank remediation according to severity, exploitability, asset importance and business exposure.
- Patch and harden: Apply updates and secure configuration changes through controlled deployment.
- Control applications: Determine which applications should be permitted, blocked or reviewed.
- Control peripherals: Define how USB devices and other peripherals may be used.
- Protect sensitive data: Identify important data and define appropriate movement and sharing controls.
- Detect malicious behaviour: Monitor endpoints for malware and suspicious activity.
- Review exceptions: Investigate failed remediation, temporary access requirements and policy overrides.
- Measure: Review security findings, exceptions, unresolved vulnerabilities and policy effectiveness regularly.
Which ManageEngine product addresses which endpoint risk?
| Endpoint Risk | Relevant ManageEngine Product | Primary Use |
|---|---|---|
| Vulnerabilities and insecure configurations | Vulnerability Manager Plus | Assessment, prioritisation, patching and remediation |
| Unauthorised or risky applications | Application Control Plus | Application allowlisting, blocklisting and execution control |
| Uncontrolled USB and peripheral access | Device Control Plus | Peripheral access and file transfer control |
| Sensitive data leaving endpoints | Endpoint DLP Plus | Data discovery, classification and movement controls |
| Malware behaviour and endpoint compromise | Malware Protection Plus | Malware detection, containment, remediation and investigation |
These products address related risks, but they should not be treated as identical or automatically necessary for every environment. The product mix should reflect the organisation’s actual endpoint exposure and operational requirements.
Why do third party applications matter?
Endpoint security must include more than the operating system. Browsers, productivity software, communication applications, development tools and other third party business software can also contain vulnerabilities or become outdated.
Vulnerability Manager Plus includes assessment and patching capabilities for supported third party applications. This matters because an organisation may have current Windows updates while still carrying exposure through an outdated browser, collaboration application or other commonly used business software.
The patching strategy should therefore consider the complete application environment, not just operating system update status.
When is Application Control Plus useful?
Application Control Plus becomes useful when the organisation needs to control which applications are permitted to execute on managed endpoints.
Allowlisting can restrict execution to approved software, while blocklisting can prevent known unwanted applications from running. ManageEngine also provides audit capabilities so administrators can understand application activity before enforcing stricter policies.
This staged approach matters. Moving immediately from unrestricted execution to a strict allowlist can interrupt legitimate applications that administrators did not know were required.
For example, a finance team may need a specific reporting tool that is not used elsewhere. An organisation that applies one allowlist to every department without software discovery could unintentionally block the application during a critical reporting period.
Tech Wave recommends using an inventory and audit stage before enforcing application controls. Build policies around departments or device groups, observe what would be affected, then move to enforcement after business exceptions have been reviewed.
When does Device Control Plus become relevant?
Device Control Plus addresses risks created by removable media and peripheral devices.
Organisations can define policies for peripheral access and file transfers, including restrictions for removable storage and other supported device types. Temporary or just in time access can also be useful where a blocked device is legitimately required for a defined task.
This balance is important. Completely blocking every USB device may sound secure, but some field teams, engineering groups or operational departments may have legitimate transfer requirements.
The better decision is to determine who needs peripheral access, which devices can be trusted, what type of files can be transferred and whether temporary access is more appropriate than permanent permission.
When should Endpoint DLP Plus be considered?
Peripheral control focuses on the device or transfer channel. Data loss prevention focuses more directly on the sensitive information itself.
Endpoint DLP Plus can discover and classify sensitive information and apply policy based controls around how that data is accessed or transferred through supported endpoint channels.
This becomes relevant where the organisation must protect information such as financial records, customer information, employee data or other confidential business content.
A strong DLP implementation should begin with data understanding. Blocking every file that contains a common number pattern or keyword can produce excessive false positives. Organisations should first identify which information is truly sensitive, where it is stored, who legitimately uses it and which transfer routes create meaningful risk.
Does stronger endpoint security mean more restrictions?
Not necessarily. Security quality should be measured by how effectively controls reduce relevant risk while allowing legitimate business activity.
A policy that blocks every application, USB device and file transfer may create substantial operational friction. A policy that permits everything creates the opposite problem.
Good endpoint security uses differentiated policies. High risk systems may justify stricter controls, while some users need approved exceptions based on their responsibilities.
Common endpoint security mistakes to avoid
Treating every endpoint as identical
A production server, finance laptop and developer workstation have different software, operational and change requirements. Security policies should reflect those differences.
Focusing only on operating system patches
Browsers, productivity tools, communication software and other third party applications should also be included in vulnerability and patching processes where supported.
Enforcing application allowlisting without an audit phase
Administrators need to understand which applications are actually used before blocking everything outside an approved list.
Blocking every removable device without understanding business use
Some teams may genuinely require removable media. Temporary or trusted device policies may be more appropriate than permanent unrestricted access or complete prohibition.
Deploying DLP before classifying sensitive data
Data protection policies should follow a clear understanding of what information requires protection and which business processes legitimately use it.
Collecting security alerts without an endpoint response process
Detection is only valuable when the organisation knows who investigates an event, how a compromised endpoint is contained and when the device can safely return to normal operation.
Where does Malware Protection Plus fit?
Malware Protection Plus addresses malicious endpoint behaviour through detection, investigation, containment and remediation capabilities.
ManageEngine documents capabilities including behaviour based detection, endpoint isolation, malicious process termination, file quarantine, recovery functions and attack chain investigation.
This solves a different problem from vulnerability management. Vulnerability Manager Plus focuses on reducing weaknesses that could be exploited. Malware Protection Plus addresses suspicious or malicious activity that is occurring or has already occurred on an endpoint.
When is broader endpoint management required?
Security controls are only part of endpoint operations. Organisations that also need software deployment, configuration management, asset visibility, remote administration and broader endpoint lifecycle management may need to assess a unified endpoint management platform such as ManageEngine Desktop Central, also known as Endpoint Central.
If the requirement is primarily patch deployment without the wider vulnerability management scope, Patch Manager Plus may also be more focused.
The correct decision therefore depends on whether the primary requirement is endpoint management, vulnerability remediation, application governance, data protection, peripheral control or malware response.
A relevant Tech Wave technology case study
The IT Pillars case study provides relevant context for organisations evaluating Tech Wave as a technology partner. IT Pillars operates in the enterprise technology solutions market, and Tech Wave supported its digital presence through web development, creative design, social media and search focused services.
This case study does not represent a ManageEngine endpoint security deployment. It demonstrates Tech Wave’s broader experience working with a technology focused business. Organisations can also explore the complete Tech Wave case study portfolio.
How can Tech Wave support an endpoint security rollout?
Tech Wave can support organisations through endpoint risk assessment, requirements analysis, solution consultation, implementation planning, policy design, pilot deployment, application inventory review, vulnerability remediation planning, data protection policy configuration, testing, administrator training and ongoing technical support.
The implementation should begin with the risks the organisation wants to reduce. From there, Tech Wave can help determine which ManageEngine endpoint controls are relevant and how policies should differ between departments, device types and levels of business sensitivity.
For organisations exploring the wider ManageEngine portfolio, Tech Wave’s guide to ManageEngine IT management solutions explains how endpoint, identity, network and service management products address different operational requirements.
Frequently Asked Questions
What is layered endpoint security?
Layered endpoint security uses multiple complementary controls, such as vulnerability management, application control, device control, data loss prevention and malware protection, to address different endpoint risks.
Is Vulnerability Manager Plus the same as antivirus software?
No. Vulnerability Manager Plus focuses on discovering, prioritising and remediating vulnerabilities and insecure configurations. Malware protection addresses malicious behaviour and endpoint compromise.
What is the difference between Device Control Plus and Endpoint DLP Plus?
Device Control Plus focuses on controlling peripheral devices and file transfers. Endpoint DLP Plus focuses on identifying sensitive information and controlling how that data is used or transferred across supported endpoint channels.
Should every company use application allowlisting?
Not automatically. Application control is particularly useful where software execution needs tighter governance. Organisations should inventory and audit legitimate applications before enforcing restrictive allowlisting policies.
Why should third party applications be included in vulnerability management?
Business endpoints use browsers, productivity tools, communication applications and other software in addition to the operating system. Outdated third party applications can therefore remain a source of vulnerability even when operating system patches are current.
Should all endpoint security policies be identical?
No. Policies should reflect endpoint purpose, user role, data sensitivity and operational impact. Critical servers may require different controls from employee laptops or specialist workstations.
Build endpoint security around actual risk
Strong endpoint security does not come from enabling every available feature. It comes from identifying specific risks, selecting the controls that address them, piloting policies and reviewing exceptions continuously.
Contact Tech Wave to discuss how Vulnerability Manager Plus and related ManageEngine endpoint security solutions can support vulnerability remediation, application governance, device control, data protection and malware response across your endpoint environment.