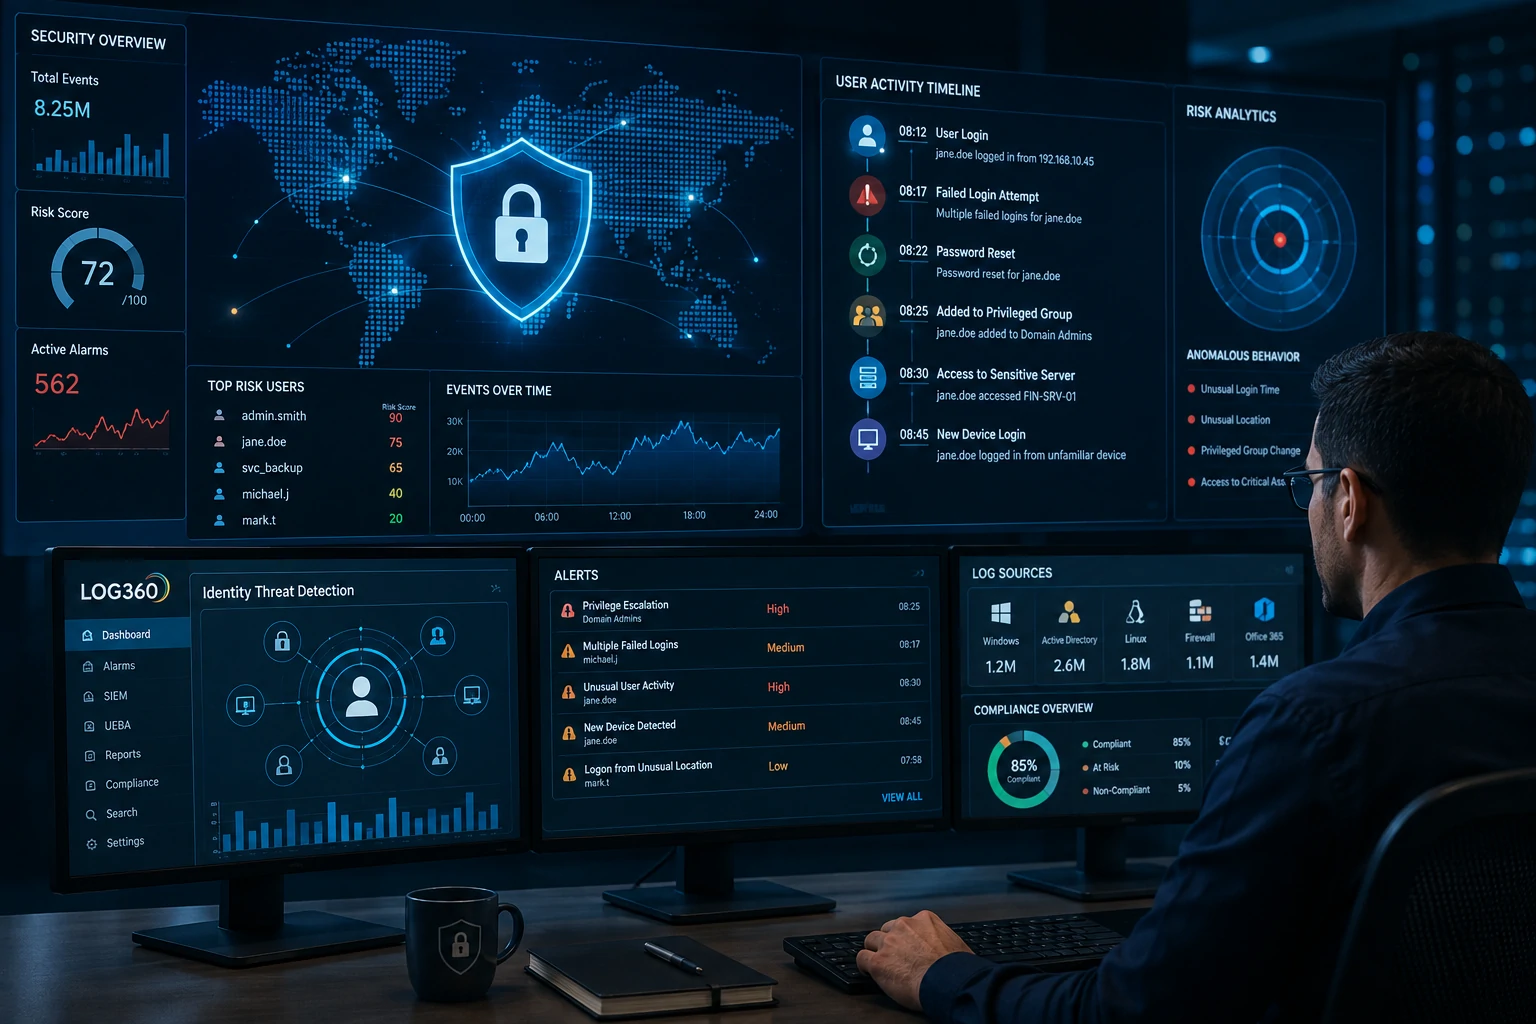
An identity attack rarely looks dangerous because of one isolated event. A successful login may be legitimate. A password reset may be routine. A new group membership may be authorised. The risk becomes clearer when several events occur together, such as an unusual login followed by a privilege change, access to a sensitive server and activity from an unfamiliar device.
This is why identity threat detection requires more than collecting security logs. Security teams need enough context to connect activity across users, endpoints, Active Directory, servers, applications and other infrastructure so they can distinguish normal administration from behaviour that deserves investigation.
What is identity threat detection?
Identity threat detection is the process of identifying suspicious behaviour involving user accounts, credentials, privileges and authentication activity by analysing events across identity systems and the wider IT environment.
The objective is to answer questions such as: Is this login normal for the user? Was a sensitive group membership changed unexpectedly? Did a dormant account suddenly become active? Is an administrator performing an unusual sequence of actions? Does activity associated with one identity also appear on another endpoint or system?
ManageEngine Log360 provides centralised security telemetry, correlation, user and entity behaviour analytics, threat detection, investigation capabilities and security analytics that can help SOC and security teams examine these patterns across supported environments.
Why are identity based attacks difficult to detect?
Attackers do not always need malware if they can obtain valid credentials. Once an account has been compromised, activity may initially resemble legitimate user behaviour. This makes identity based threats particularly dependent on context.
Consider an organisation with 500 employees, remote users and several administrators. A finance employee logging in from a new device may be perfectly legitimate. The same login becomes more concerning if it is followed by repeated authentication failures, access outside the employee’s normal pattern and unexpected privilege related activity.
No single event necessarily proves compromise. The investigation becomes stronger when the security platform can correlate multiple signals and help analysts understand the sequence.
Which identity signals should security teams monitor?
Identity monitoring should reflect the organisation’s actual environment and risk profile rather than attempting to alert on every possible event.
Useful signals may include:
- Unusual authentication patterns
- Repeated failed logins followed by a successful login
- Changes to privileged or administrative groups
- Suspicious password reset activity
- Unexpected privilege escalation
- Activity from accounts that are normally inactive
- Access outside normal user behaviour
- Administrative actions occurring from unexpected systems or locations
- Sequences of events that together indicate a possible attack path
Log360 includes correlation based detections, anomaly models, threat intelligence context and user and entity behaviour analytics. ManageEngine also provides object level filtering for Active Directory and Microsoft 365 related detections, allowing teams to narrow certain rules according to users, groups or organisational units.
Tech Wave implementation recommendation: begin with identity events that could materially affect important systems. A security team usually gains more value from well tuned detection around privileged groups, critical administrators and sensitive identities than from enabling every available alert without prioritisation.
A practical identity threat investigation workflow
A repeatable investigation process helps analysts move from an alert to an evidence based decision rather than reacting differently to every event.
- Collect: Ingest relevant security logs from identity systems, endpoints, servers, network infrastructure and supported cloud services.
- Detect: Apply correlation, behavioural analytics and appropriate detection rules to identify suspicious activity.
- Prioritise: Determine whether the affected identity, device or system has elevated business or security importance.
- Validate: Check whether the event can be explained by an approved change, legitimate administrator action or known user behaviour.
- Correlate: Review related logins, account changes, devices, IP addresses and events around the same time.
- Investigate: Build a timeline of what occurred before and after the alert.
- Respond: Escalate or contain the activity according to the organisation’s incident response process.
- Tune: Adjust detection logic, exclusions or thresholds when the investigation reveals avoidable noise.
- Review: Use the incident to identify monitoring gaps, missing log sources or policies that require improvement.
Does collecting more logs automatically improve security?
No. Larger log volumes do not automatically create better threat detection.
If important identity sources are missing, timestamps are inconsistent, detection rules are poorly tuned or nobody owns the resulting alerts, increasing ingestion may simply create more data for analysts to search.
The better approach is to start with detection objectives. For example, if the organisation wants to identify suspicious administrator activity, it should first confirm that relevant authentication, Active Directory and critical system events are being collected reliably. Additional sources can then be introduced when they improve investigation context.
| Monitoring Approach | Potential Value | Risk to Avoid |
|---|---|---|
| Collect every available source immediately | Broad potential visibility | High noise and unclear priorities |
| Start with critical identity and infrastructure sources | Focused detection and easier validation | Important secondary context may initially be missing |
| Enable every detection rule | Large initial detection coverage | Alert fatigue and unnecessary investigations |
| Tune rules around actual risks | More relevant alerts | Over tuning may hide useful signals if exceptions are poorly designed |
How does behaviour analytics add context?
Static rules are useful when a known sequence or condition should always trigger attention. Behaviour based detection addresses a different problem by identifying activity that deviates from expected patterns for a user or entity.
For example, an administrator may legitimately access multiple servers. The activity may deserve greater attention if the account suddenly authenticates at an unusual time, interacts with systems it does not normally use and performs privilege related actions shortly afterwards.
Log360’s user and entity behaviour analytics can help surface deviations for investigation. Behaviour analytics should not be treated as proof that an account is compromised. It provides investigative context that analysts should validate alongside other evidence.
Why does correlation matter during an identity investigation?
A suspicious identity event becomes more useful when analysts can connect it with activity elsewhere in the environment.
Imagine that a privileged group membership changes at 10:05. At 10:09, the affected account authenticates to a critical server. At 10:14, another security event occurs from the same endpoint. Looking at each record independently makes investigation slower. Correlation allows the team to assess whether these events belong to one meaningful sequence.
Log360 includes correlation based threat detection and investigation capabilities that allow security teams to move from alerts towards related logs, users, devices and event context.
When is ADAudit Plus relevant alongside Log360?
ManageEngine ADAudit Plus becomes particularly relevant when an organisation needs deeper auditing of Active Directory changes, Windows logons, file server activity and related identity events.
Log360 addresses the broader SIEM and security analytics requirement by correlating information across multiple parts of the IT environment. ADAudit Plus is more specialised around Active Directory and Windows auditing.
This distinction matters during solution design. An organisation primarily concerned with detailed Active Directory change auditing may begin with ADAudit Plus. A SOC that needs to connect identity signals with events from servers, endpoints, network devices, cloud services and other security sources has a broader SIEM requirement where Log360 becomes more relevant.
Organisations evaluating wider Active Directory management and identity governance requirements can also review ManageEngine AD360, which addresses identity administration, lifecycle management, auditing and related Active Directory requirements through a broader identity management suite.
Common mistakes when building identity threat detection
Alerting on every administrative change
Administrative changes are not automatically malicious. Alerts should reflect sensitive actions, unusual context and the organisation’s actual risk priorities.
Ignoring service accounts
Identity monitoring should not focus only on employee accounts. Service accounts and other non human identities may also hold important permissions and should have clearly understood behaviour and ownership.
Leaving test accounts inside high priority detection rules
Development and test activity can create unnecessary noise. Log360’s filtering and rule tuning capabilities should be used carefully to remove known low value activity without suppressing relevant threats.
Collecting logs without validating ingestion
A configured source is not necessarily a reliable source. Teams should check whether events arrive consistently, contain the expected fields and use timestamps that support accurate investigation.
Creating alerts without ownership
Every high priority alert should have a defined response path. If nobody knows who validates an identity alert or when it should be escalated, the detection rule has limited operational value.
Assuming AI removes the need for analysts
Log360 includes AI assisted investigation capabilities, but automated summaries and investigation support should complement analyst judgement rather than replace validation of business context and incident evidence.
How should organisations reduce identity alert noise?
Alert reduction should focus on relevance rather than simply lowering the number of notifications.
Security teams can classify privileged identities, exclude clearly documented test activity where appropriate, tune detection thresholds, prioritise sensitive organisational units and review repeated false positives. The goal is to preserve meaningful detection coverage while reducing activity that repeatedly proves benign.
Tech Wave recommends reviewing alert quality after the initial deployment period instead of treating the first configuration as final. Analysts should identify which rules regularly produce useful investigations, which rules need more context and which log sources are creating gaps or unnecessary noise.
What should be defined before implementing Log360?
Before deploying a SIEM broadly, organisations should define the security questions they expect it to answer.
- Which identities and systems are most sensitive?
- Which attacks or suspicious behaviours are the highest priorities?
- Which log sources provide the evidence required for those use cases?
- Who owns each category of alert?
- Which events require immediate escalation?
- How long should security information be retained?
- Which dashboards and reports are useful for security operations?
- How will detection rules be reviewed and tuned over time?
A practical rollout might begin with Active Directory, critical Windows systems, selected endpoints and key security infrastructure. Once ingestion quality, correlation and investigation workflows are validated, the organisation can expand coverage according to its risk priorities.
A relevant Tech Wave technology case study
Tech Wave’s work extends beyond individual product deployments to supporting technology focused businesses with their wider digital and technology presence. The IT Pillars case study provides an example of Tech Wave’s work with IT Pillars, a company operating in the enterprise technology solutions market.
This case study is useful context for organisations evaluating Tech Wave as a technology partner, while the specific Log360 implementation approach should always be designed around the customer’s own security architecture, log sources, detection priorities and incident response model. You can also explore the broader Tech Wave case study library.
How can Tech Wave support Log360 implementation?
Tech Wave can support organisations with security use case definition, log source assessment, solution consultation, Log360 implementation, collection configuration, correlation rule tuning, identity focused detection design, dashboards, alert routing, investigation workflows, reporting, training and ongoing technical support.
The implementation should begin with the incidents the security team needs to recognise and investigate. The platform can then be configured around those questions instead of collecting large volumes of data without a defined operational purpose.
For wider context on the ManageEngine portfolio, organisations can also review Tech Wave’s complete guide to ManageEngine IT management solutions.
Frequently Asked Questions
Can Log360 detect compromised user accounts?
Log360 can identify suspicious account activity through correlation, behaviour analytics, anomaly detection and other security detections. An alert indicates activity that requires investigation rather than automatically proving that an account has been compromised.
What identity events should a SIEM monitor?
Important events may include unusual authentication, privilege changes, administrative group modifications, suspicious password resets and behaviour that deviates from expected user or entity patterns.
What is the difference between Log360 and ADAudit Plus?
Log360 provides broader SIEM, security analytics and threat investigation across multiple log sources. ADAudit Plus specialises more deeply in Active Directory, Windows logon and related auditing use cases.
Does Log360 use behaviour analytics?
Yes. Log360 includes user and entity behaviour analytics that can identify deviations from established behaviour and provide additional context for security investigations.
Should every security alert be investigated with the same priority?
No. Priority should consider the affected identity, system sensitivity, privilege level, supporting evidence and potential business impact.
Can Log360 reduce false positives?
Detection rules, filtering, thresholds and anomaly models can be tuned to the organisation’s environment. Tuning should be reviewed regularly so that noise is reduced without hiding important security activity.
Turn identity events into actionable security context
Identity security depends on recognising meaningful patterns, not simply storing authentication records. A useful SIEM programme connects identity events with the systems, devices and actions surrounding them so analysts can investigate suspicious behaviour with better context.
Contact Tech Wave to discuss how Log360 can support identity focused threat detection, correlation, behavioural analytics, alert tuning and investigation workflows across your security environment.