A privileged account can change security settings, install software, modify configurations, access sensitive systems or administer critical infrastructure. That level of authority is necessary for many IT tasks, but it also means that stolen, shared or poorly governed privileged credentials can create significantly greater exposure than an ordinary user account.
The challenge becomes more complex when administrators, service accounts, infrastructure teams and external vendors all require different levels of privileged access. Organisations need to know which privileged accounts exist, who owns them, who is allowed to use them, how long access should remain available and what happened during each privileged session.
What should a privileged access strategy control?
A privileged access strategy should control privileged identities, credentials, access requests, elevated permissions and administrative sessions according to the sensitivity of the systems involved.
The objective is not simply to place administrator passwords inside a vault. Effective privileged access management should address the full access lifecycle, from discovering privileged accounts through granting access, monitoring activity, rotating credentials and reviewing exceptions.
ManageEngine PAM360 provides capabilities for privileged account discovery, central credential vaulting, password rotation, access controls, just in time privilege elevation, secure remote access, privileged session monitoring and recording, and audit reporting. These capabilities become valuable when they are configured around a clearly defined governance model rather than deployed as isolated security features.
Why is standing privileged access a problem?
Standing privilege means an account keeps elevated permissions even when those permissions are not currently required. The longer powerful access remains available, the larger the opportunity for credentials to be misused, compromised or applied outside the intended task.
For example, a database administrator may need elevated access during a scheduled maintenance activity but may not need the same privilege continuously throughout the week. Similarly, an external support engineer may require temporary access to a server for troubleshooting without needing permanent administrator rights.
PAM360 supports just in time controls that can provide higher privileges when required and revoke those permissions after the defined period. This allows organisations to design access around actual operational need instead of granting permanent elevated rights by default.
Start with privileged account discovery
An organisation cannot govern privileged access effectively if it does not know where privileged accounts exist. Discovery should therefore come before aggressive password rotation, session policies or automation.
A useful inventory should identify:
- Privileged accounts associated with critical servers and infrastructure
- Domain and local administrator accounts
- Service accounts and accounts used by applications or scheduled processes
- Accounts used to manage network and infrastructure devices
- Privileged credentials used by external suppliers or support teams
- Account owners and the business or technical systems they support
PAM360 supports discovery of privileged resources and privileged accounts across supported resource types, with options for on demand and scheduled discovery.
Tech Wave implementation recommendation: do not treat discovery as an automatic instruction to onboard every account immediately. Review discovered accounts first, identify ownership and determine whether each account is active, required, duplicated, obsolete or connected to an application dependency. This prevents the PAM environment from becoming a repository of poorly understood privileged identities.
A practical PAM360 privileged access workflow
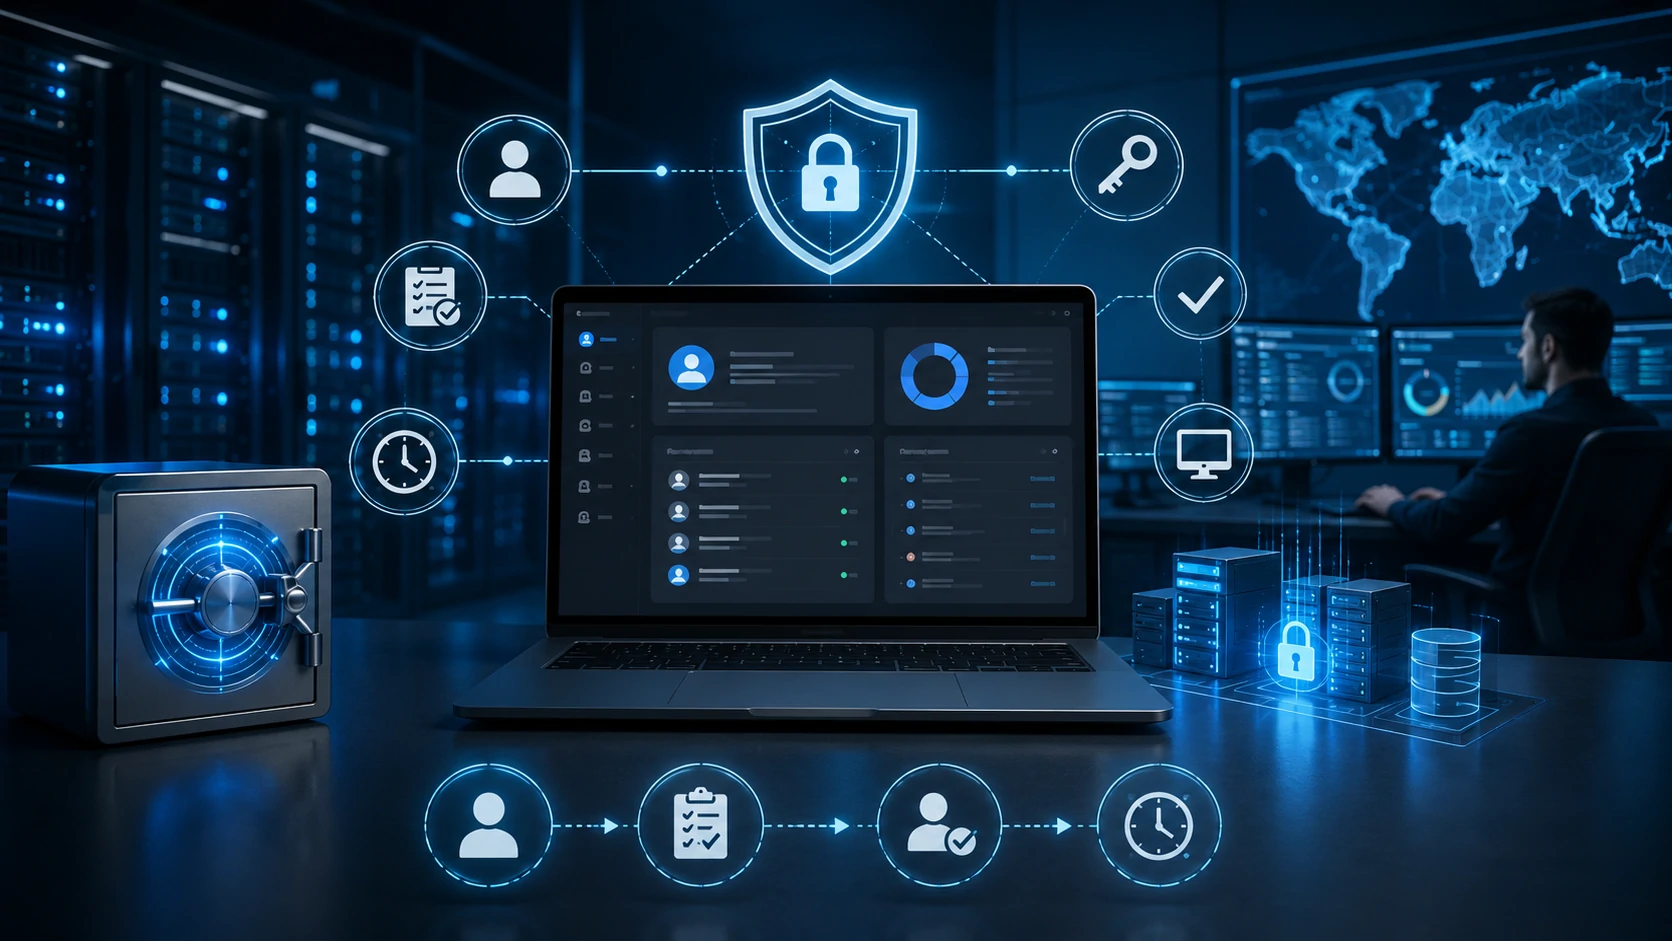
A mature privileged access process should connect governance with the actual administrator experience. A practical workflow can follow these stages:
- Discover: Identify privileged systems, resources and accounts within the agreed project scope.
- Classify: Assign system importance, account ownership, user groups and access sensitivity.
- Onboard: Add approved privileged credentials to the central vault and define appropriate management policies.
- Request: Require users to request privileged access where approval is appropriate.
- Approve: Route sensitive access according to defined ownership and business rules.
- Grant: Provide the required level of access, using time limited or just in time privilege where appropriate.
- Monitor: Monitor or record sensitive privileged sessions according to organisational policy.
- Rotate: Change privileged passwords or credentials according to approved rotation policies and system dependencies.
- Review: Analyse access activity, exceptions, unusual behaviour and policy effectiveness regularly.
This workflow is more useful than simply enabling every PAM feature. Each control should answer a specific question about who needs access, why access is required, which system is involved and what evidence must remain afterwards.
Should every privileged request require approval?
No. Requiring the same approval process for every administrative action can create unnecessary delays without providing proportionate security value.
The approval model should reflect risk. Routine access to a lower sensitivity administration environment may use a simpler policy, while production infrastructure, critical databases or highly privileged domain access may justify stronger approval and session controls.
| Scenario | Possible Control | Decision Consideration |
|---|---|---|
| Routine administration of a defined system | Role based access with policy controls | Access is predictable and ownership is already established |
| Temporary vendor maintenance | Approval, time limited access and session monitoring | The user is external and access is required for a defined period |
| Elevation to sensitive administrative rights | Just in time privilege with approval where appropriate | Permanent privilege may not be necessary |
| Access to critical production infrastructure | Stricter approval and session recording | The potential operational and security impact is higher |
Why credential vaulting alone is not enough
A password vault solves an important problem by centralising sensitive credentials and controlling who can access them. Privileged access management, however, must also consider what happens before, during and after the privileged activity.
For example, allowing an administrator to retrieve a password may still expose that credential unnecessarily. Where the use case supports it, PAM360 can broker secure remote sessions so users can connect to target resources without directly receiving the underlying privileged credential.
Session monitoring and recording then provide additional accountability. Recording every session is not automatically necessary for every resource, but it can be valuable for systems where administrative actions need to be reviewed during investigations, security analysis or governance exercises.
Plan password rotation around dependencies
Automatic password rotation is valuable only when organisations understand what depends on the credential being changed.
A human administrator account may be relatively straightforward to rotate. A service account can be more complicated because applications, scheduled tasks, services or other technical processes may rely on the same credential.
Changing a password without understanding those dependencies can interrupt legitimate operations. The correct approach is to identify dependent systems, test rotation behaviour and define exception procedures before applying aggressive rotation schedules.
From an implementation perspective, Tech Wave recommends piloting password rotation on a controlled group of accounts before expanding the policy. Include both normal administrator accounts and representative service accounts in testing so that operational dependencies become visible before wider deployment.
Common PAM implementation mistakes to avoid
Starting with the technology instead of the privileged account inventory
Configuring vaults and policies before identifying account owners and critical systems can produce inconsistent access rules and unmanaged exceptions.
Using identical controls for every system
A development server and a critical production environment do not necessarily require the same approval, monitoring or session recording policy. Controls should reflect the consequences of privileged misuse.
Rotating service account passwords without dependency testing
Service credentials may be referenced by applications or automated processes. Rotation should be tested before schedules are applied broadly.
Recording sessions without defining who reviews them
Collecting large amounts of privileged session data provides limited value if nobody is responsible for reviewing suspicious activity or responding to alerts.
Giving vendors permanent administrator access
External support requirements are often temporary. Time bound access and appropriate approval can be more suitable than leaving privileged accounts available indefinitely.
Creating too many alerts
An alert policy should identify activities that genuinely require investigation. Excessive low value notifications can make important events harder for security teams to recognise.
PAM360, Password Manager Pro or Access Manager Plus?
The correct choice depends on the scope of the privileged access problem. Organisations should avoid selecting a platform simply because it contains the largest feature set.
| Primary Requirement | Relevant ManageEngine Solution | When It Becomes Useful |
|---|---|---|
| Broad privileged access governance | PAM360 | When credentials, access policies, privilege elevation, remote sessions and monitoring need to be governed through a broader PAM approach |
| Central privileged credential management | Password Manager Pro | When the central requirement is storing, controlling, sharing and rotating privileged credentials |
| Secure privileged remote access | Access Manager Plus | When the primary requirement is brokering and controlling remote privileged sessions with monitoring and recording |
These products address related privileged access challenges, but they should not be treated as interchangeable. Requirements analysis should determine whether the organisation mainly needs credential governance, remote session control or a broader privileged access management programme.
For organisations evaluating ManageEngine beyond privileged access, Tech Wave’s complete guide to ManageEngine IT management solutions provides wider context on the product families available for identity, security, endpoint management and IT operations.
What should organisations define before implementing PAM360?
Before production deployment, organisations should document the systems and privileged accounts in scope, ownership, access roles, approval requirements, credential rotation policies, vendor access rules, session monitoring requirements and the teams responsible for reviewing alerts and audit information.
A practical pilot might begin with a defined group of infrastructure administrators and a limited set of Windows or Linux servers. The organisation can test account onboarding, approval behaviour, credential rotation, session launch and reporting before adding production databases, network devices, service accounts or vendor access.
This staged approach makes policy problems easier to correct and provides administrators with a clearer operating model before the privileged access programme expands.
How can Tech Wave support a PAM360 rollout?
Tech Wave can support organisations with privileged account discovery planning, requirements analysis, solution consultation, PAM360 implementation, vault structure design, access policy configuration, approval workflow design, credential rotation planning, session monitoring policies, pilot testing, administrator training, reporting setup and ongoing technical support.
The implementation should reflect how administrators and vendors actually access critical systems. A well designed PAM project does not simply place controls between users and infrastructure. It provides the required access while making ownership, approval, accountability and exceptions clear.
Frequently Asked Questions
What is privileged access management?
Privileged access management is the process of discovering, securing, controlling, monitoring and auditing accounts and sessions that have elevated access to critical systems and infrastructure.
What does PAM360 manage?
PAM360 provides capabilities for managing privileged credentials, access controls, password rotation, just in time privileges, remote privileged sessions, monitoring, recording and audit information across supported environments.
Does PAM360 support just in time privileged access?
Yes. PAM360 supports just in time privilege controls that can provide elevated rights when required and remove those privileges after the defined access period.
Can PAM360 hide privileged passwords from administrators?
For supported secure remote access scenarios, PAM360 can broker connections using credentials stored in its vault so that users do not need to receive or manually enter the underlying privileged password.
Should every privileged session be recorded?
Not necessarily. Session recording requirements should reflect the sensitivity of the resource, investigation requirements, internal policy and applicable governance obligations.
What is the difference between PAM360 and Password Manager Pro?
Password Manager Pro focuses strongly on privileged credential vaulting, access control and password management. PAM360 addresses a broader privileged access management scope that includes credential governance, privilege controls, secure remote access and session oversight.
Where should a PAM360 implementation start?
Start by identifying privileged systems and accounts, assigning owners, classifying risk, defining access policies and selecting a controlled pilot group before expanding automation and privileged access controls across the environment.
Build privileged access around governance, not permanent privilege
The strongest privileged access programme is not the one with the greatest number of restrictions. It is the one that gives administrators the access required to perform legitimate work while reducing unnecessary standing privilege, protecting credentials and preserving clear accountability.
Contact Tech Wave to discuss how PAM360 can support privileged account discovery, credential vaulting, just in time access, approval workflows, password rotation and privileged session governance across your IT environment.